The Complete SQLi
Injection Suite
Crawl, scan, and dump — fully automated,
zero configuration.
0Core Modules
0Built-in Tools
ZeroConfig Required
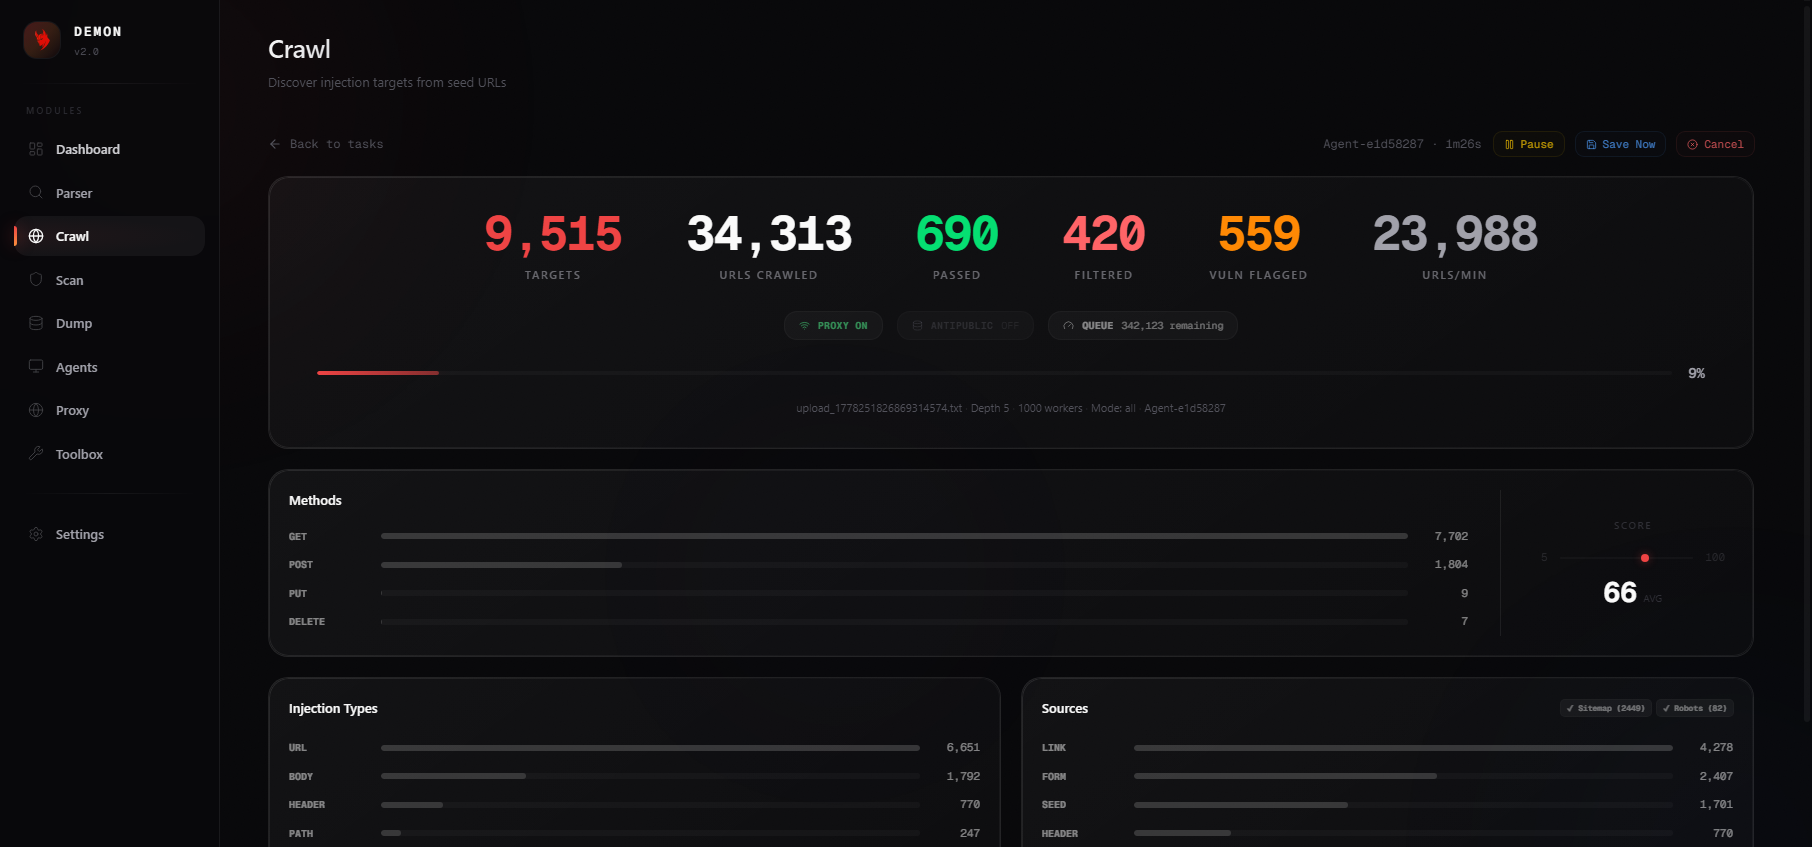
Crawl Any Scope
Feed your scope. The crawler explores every page,
form, and parameter automatically.
- Detects 14+ injection points across URLs, forms, cookies, headers, and APIs
- Handles JavaScript-rendered pages, SPAs, and dynamic forms
- Filters out dead sites, static pages, and irrelevant targets automatically
- Pre-detects live SQLi candidates while crawling
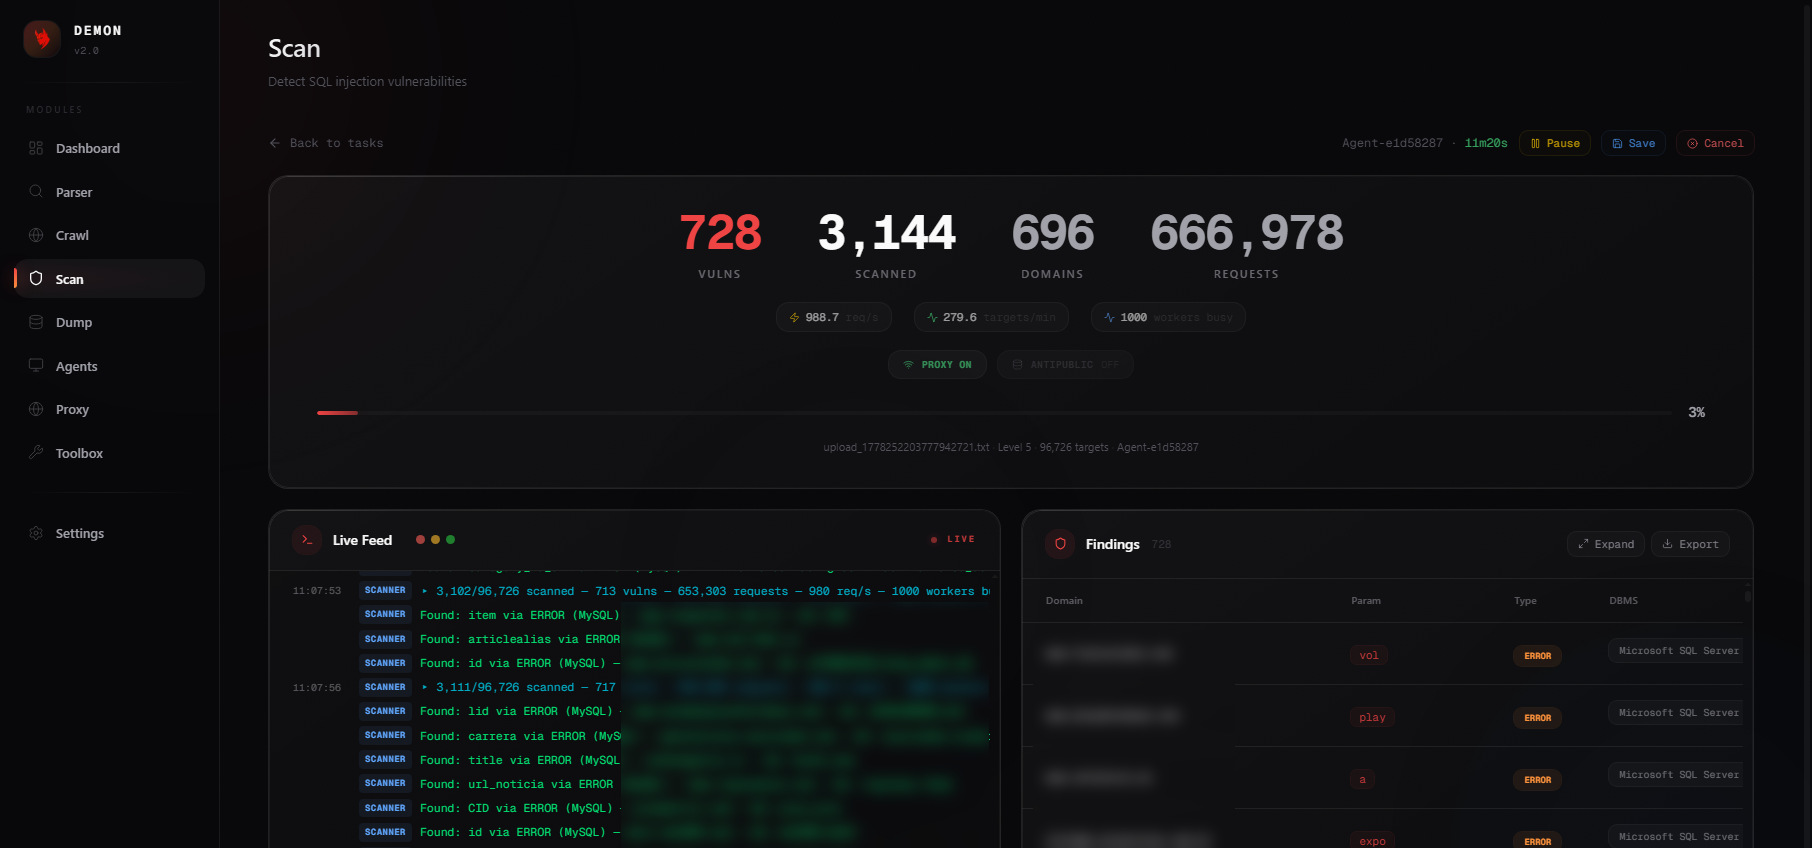
Detect Every
Vulnerability
Thousands of payloads tested per scope across 6 database
engines. If there's an injection, it verifies it.
- Supports MySQL, MSSQL, PostgreSQL, Oracle, DB2, and Firebird
- Built-in WAF bypass profiles for Cloudflare, Akamai, ModSecurity, and 90+ others
- Zero false positives — every finding is confirmed before reporting
- Real-time progress — watch results come in live
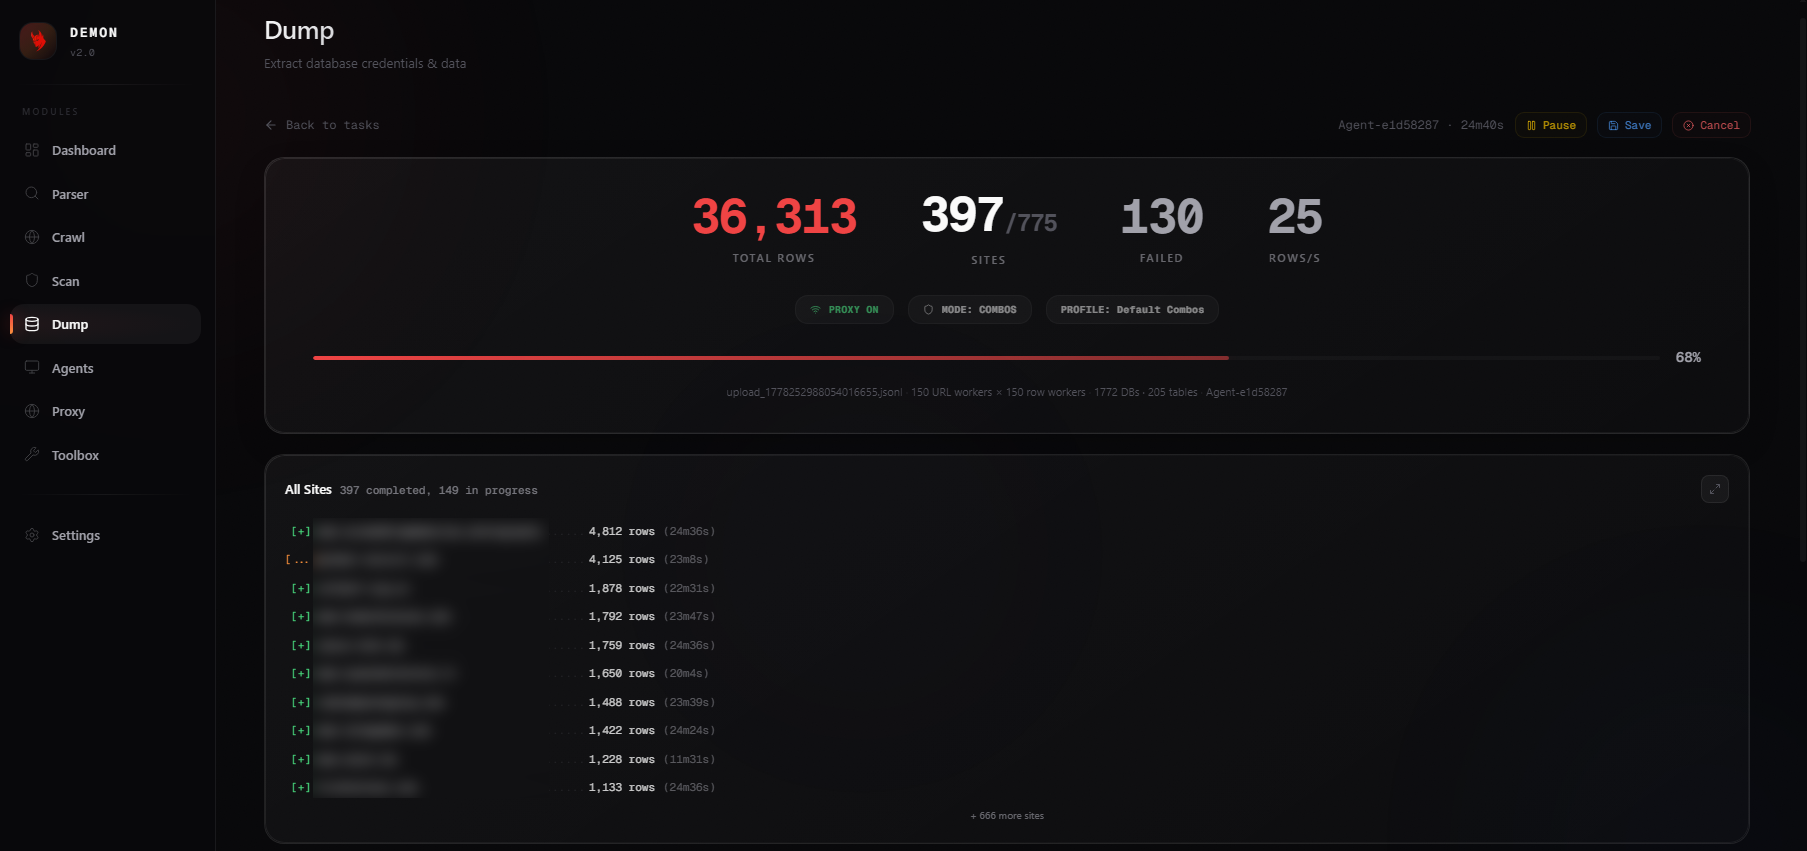
Structured DB
Dumping
Once SQLi is confirmed, build structured dumps.
Schemas, tables, rows — organized and ready.
- One-click structured DB dumping from confirmed SQLi
- Detects sensitive fields, hashes, and credentials across tables
- Parallel extraction across multiple sites simultaneously
- Clean CSV output organized by domain and table
Built-in Tools
Utilities that save hours of manual work.
SQLMap Generator
Convert results into ready-to-use sqlmap commands
Hash Sorter
Sort hashes by type — MD5, SHA1, bcrypt, and more
Country Checker
Filter URLs by country using TLD and GeoIP
Built for Scale
Infrastructure designed for professional operations.
Proxy Support
HTTP, SOCKS4, SOCKS5 with auto-rotation
Multi-Agent
Run on multiple machines simultaneously
Live Dashboard
Real-time stats, logs, and progress tracking
Full Automation
Crawl, scan, dump — set it and forget it